Multisig vs MPC wallets are often presented as competing answers to the same security problem: how can several people or devices control digital assets without trusting one private key? Both can divide transaction authority, but they enforce that division in fundamentally different places.
Multisig generally asks a blockchain or smart contract to verify multiple signatures. MPC distributes the signing process itself, allowing participants to produce one valid signature without placing a complete private key in one location. That distinction affects transparency, compatibility, recovery, governance, and the kinds of failure an organization must prepare for.
Multisig vs MPC Wallets Divide Authority Differently
A conventional wallet uses one private key to create a signature accepted by the blockchain. Whoever controls that key can normally authorize transactions, making the key a valuable target and a potential single point of failure.
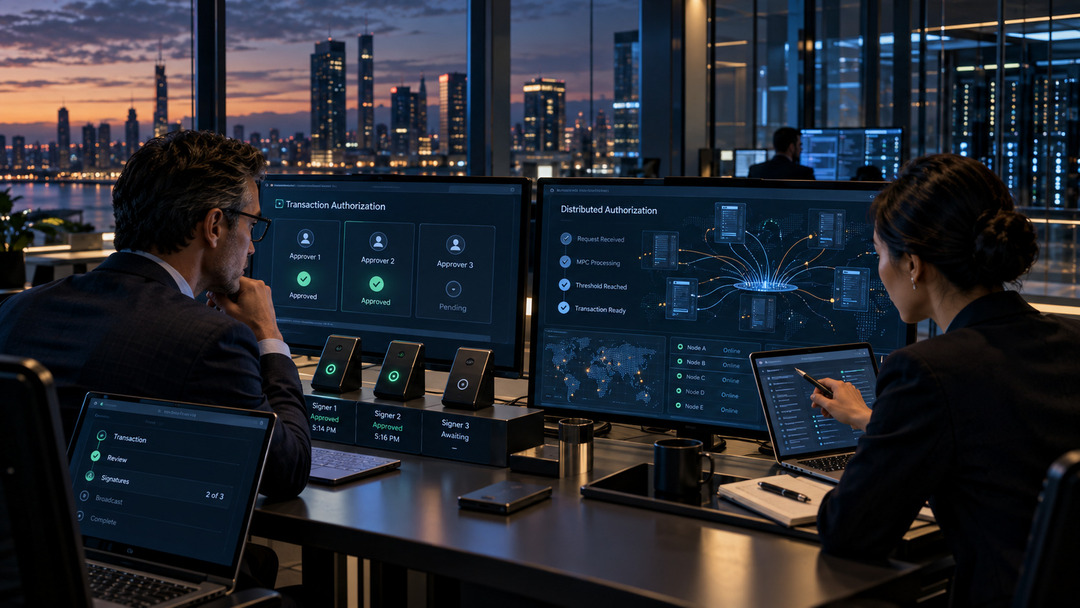
Multisig replaces that single authorization requirement with several independent keys. A typical two-of-three arrangement allows three designated signers to participate but requires signatures from any two before funds can move. The signing threshold is enforced by the asset’s native protocol or by smart-contract logic.
MPC usually takes a different route. Participants hold cryptographic shares and cooperate in a protocol that generates a valid signature. In a properly designed threshold-signing system, the complete signing secret does not need to be assembled on one device.
Both approaches establish shared transaction authority. They do not, however, create identical evidence, recovery options, or operational dependencies.
Multisig Makes the Approval Structure Visible
Bitcoin supports scripts requiring a specified number of signatures before funds can be spent. Its multisignature transaction rules describe the familiar m-of-n arrangement, in which m represents the minimum signatures required from n available public keys.
Because multiple signatures or smart-contract actions are evaluated on-chain, multisig can provide strong public evidence of how a transaction was authorized. Auditors, participants, and outside observers may be able to examine the wallet’s threshold and transaction history, depending on the network and implementation.
That visibility is valuable for organizations that prioritize verifiable governance. A treasury might distribute keys among executives, independent directors, and an outside custodian so no single participant can transfer funds alone.
Visibility can also disclose operational information. An observer may learn that an address uses shared control, see which contract governs it, or infer changes in signer activity. Transactions may require more blockchain data and higher fees on networks where each signature is recorded separately.
Signer changes can create additional work. Depending on the design, replacing a departed employee may require updating a smart contract, creating a new wallet, or transferring assets to an address controlled by a new signer group.
MPC Moves Cooperation Into the Signing Process
Multi-party computation is a broader field than cryptocurrency custody. In wallet systems, it is commonly used through threshold cryptography so several participants can jointly perform a signing operation without one participant possessing the complete secret.
The threshold cryptography framework describes this model as distributing trust across multiple parties while performing cryptographic operations. Wallet implementations may generate shares through a distributed process rather than creating a complete key first and dividing it afterward.
When enough authorized shares participate, the system produces a signature that the blockchain can verify using its ordinary signature rules. The network may see one standard signature rather than an on-chain list of every approving participant.
This can make MPC adaptable across networks that support the relevant signature algorithm but lack native multisig features. It may also allow participants or shares to be refreshed without changing the public wallet address, although that capability depends on the specific protocol and implementation.
The tradeoff is reduced on-chain visibility. The blockchain proves that a valid signature authorized the transaction, but it may not reveal how many parties approved it or which internal policy produced it. Evidence must instead come from access records, approval logs, system controls, and audits.
Readers who need a foundation before comparing these architectures can review how private keys secure wallets and authorize blockchain transactions.
The Best Choice Depends on the Control Objective
The useful question is not which technology sounds more advanced. It is where an organization wants the authorization threshold enforced and how it intends to prove that its controls worked.
| Decision factor | Multisig | MPC wallet |
|---|---|---|
| Authority structure | Several independent private keys | Distributed shares participate in signing |
| Enforcement point | Blockchain protocol or smart contract | Cryptographic signing protocol |
| Blockchain output | Multiple signatures or contract execution may be visible | Usually appears as one valid signature |
| Network compatibility | Requires native or contract-based multisig support | Can work where the resulting signature type is supported |
| Signer changes | May require contract changes or asset migration | Share refresh may preserve the wallet address |
| Audit evidence | On-chain activity plus internal records | Primarily internal approval and protocol records |
| Main operational concern | Key coordination and signer availability | Protocol implementation and system coordination |
Multisig may suit a treasury that values visible, independently verifiable approvals and operates on a network with mature multisig support. MPC may fit an institution that needs consistent workflows across several networks, private approval structures, or more flexible participant management.
Neither label answers who runs the software, stores backups, approves recovery, or controls administrative privileges. Governance determines real control.
Security Depends on More Than the Threshold
A two-of-three policy sounds resilient because one missing participant does not stop legitimate access. Yet the arrangement fails if an attacker compromises two keys or shares, if two insiders collude, or if recovery procedures allow one administrator to bypass the intended threshold.
Endpoints remain important. Multisig cannot compensate for several signers approving a malicious transaction displayed inaccurately by compromised devices. MPC cannot protect assets if its participants rely on the same vulnerable authentication system or if implementation flaws undermine the signing protocol.
Availability creates a separate risk. Participants may lose devices, leave an organization, become unreachable, or disagree during an urgent transfer. A secure design must specify replacement, succession, emergency access, and recovery before those events occur.
Backups also require care. Storing several keys or shares in one location can recreate the concentration the architecture was meant to remove. Logical separation without operational separation offers limited protection.
The Next Test Is Recovery, Not Marketing
Wallet providers frequently emphasize the absence of a single private key or the protection offered by multiple signatures. Buyers should press beyond those claims and request a complete authority map.
That map should identify who can initiate transactions, who approves them, what each participant sees before approval, where devices and backups reside, and whether an administrator can alter policies. It should also explain what happens when a signer disappears, a device is compromised, or the provider becomes unavailable.
For MPC, reviewers should examine the threshold protocol, key-generation process, share-refresh procedure, audit records, and dependence on coordinators or proprietary services. For multisig, they should inspect the wallet script or contract, signer distribution, upgrade authority, transaction-decoding tools, and migration plan.
Independent testing and documented recovery exercises deserve more weight than broad claims that one architecture eliminates key risk. Both merely redistribute the attack surface. Their safety depends on whether the surrounding controls preserve that distribution during routine transactions and stressful recovery events.
The practical lesson from multisig vs MPC wallets is that shared control is an architecture, not a feature label. Multisig places approval evidence closer to the blockchain, while MPC embeds cooperation inside the cryptographic signing process. The safer choice is the one whose failure modes, audit trail, recovery path, and governance structure match the assets and organization it must protect.
Frequently asked questions
Can an MPC wallet also use multisig?
Yes. An organization can place an MPC-controlled signer inside a multisig arrangement. The MPC system governs one signature, while the blockchain or smart contract still requires additional independent signatures.
Is an MPC wallet automatically non-custodial?
No. Custody depends on who controls enough shares, policies, recovery methods, and administrative systems to authorize transactions. An MPC design can be custodial, non-custodial, or structured as shared custody.
What happens if one signer or MPC participant is unavailable?
A threshold design can continue if enough authorized participants remain available. Access may stop when availability falls below the required threshold, making tested replacement and recovery procedures essential.