The XRP Ledger bridge exploit on August 9, 2026, was not a break in XRP Ledger consensus or validator security. It was a bridge-verification failure: off-chain relayer software accepted payment metadata as proof of a deposit without confirming the payment destination. That distinction matters because bridge users, developers, auditors, and operators face different risks depending on whether the fault sits in base-chain security or in the systems that interpret chain activity.
Jordan Malik’s assessment is cautious: the facts available support a clear technical failure, but not every operational detail has been publicly disclosed. The reported loss was about 199,916.3 XRP, roughly $200,000 at the time of reporting, and the reserve fell from about 200,410 XRP to about 493.5 XRP. The episode lasted 97 minutes and involved 94 payout transactions. Those figures point to a failure of validation, monitoring, and emergency response, not to a single missing checkbox.
What The XRP Ledger bridge exploit Changed
XRP Ledger bridge exploit Timeline
On August 9, 2026, the xrpl-tx bridge was drained over a 97-minute window that began at about 19:16 UTC. According to SigIntZero’s technical review, the bridge processed 94 payouts, the bridge’s multisignature process required 17 of 28 relayers, and neither validator keys nor private keys were reported compromised SigIntZero analysis. The relayers signed transactions because their software concluded that deposits had occurred. The unsafe part was not the final signature step; it was the input data that the signing process trusted.
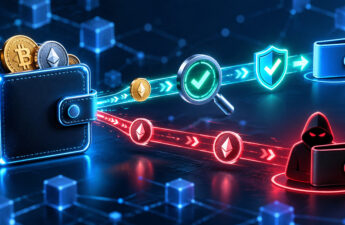
The bridge reserve was nearly depleted because the software treated transactions containing correct memo data as if they were legitimate incoming deposits. Memo fields can be set by users, so they are not reliable by themselves as settlement proof. A secure bridge verifier must check delivery details that cannot be substituted by attacker-controlled metadata. In this case, the missing control was destination validation: the software did not confirm that the payment was actually addressed to the bridge reserve account before authorizing corresponding activity.
Why The Base Ledger Was Not The Failed Component
The XRP Ledger itself was not reported breached. Ledger integrity, validators, and consensus were not the mechanism that allowed the reserve to be drained. The failure sat in software that observed ledger activity and converted those observations into bridge-side accounting decisions. This is a recurring pattern in cross-chain systems: assets can be secure on their native ledger while the representation of those assets on another chain becomes unsafe due to faulty interpretation, stale state, or weak reconciliation.
The XRP Ledger feature involved in the analysis was DefaultRipple, which relates to rippling of issued-token payments across trust lines. In the reported incident, transactions that were not valid bridge deposits could still appear in a way that the bridge software interpreted as relevant to the bridge account. The technical lesson is not that DefaultRipple alone caused the loss. The safer reading is that bridge software must understand protocol-specific behavior and verify actual delivered value, not just transaction visibility or metadata.
Relayer Logic And Memo Trust Failure
Why Multisignature Did Not Stop The Drain
The XRP Ledger bridge exploit showed that a multisignature quorum can approve unsafe transactions if the logic feeding the quorum is wrong. A 17-of-28 relayer threshold can reduce single-key and small-group compromise risk, but it does not independently prove that a deposit occurred. If most relayers run the same flawed parser or rely on the same unsafe state, they can reach agreement on a false premise. Consensus among relayers is not the same as correctness of the deposit detector.
CoinDesk reported that the bridge software mistook fake deposits for real ones, that the operator halted the bridge after the incident, and that the vulnerable code had been identified and patched while forensic specialists were engaged and an IC3 complaint was filed CoinDesk report. That response was necessary, but it also left affected users exposed to uncertainty while the operator worked through reserve shortfall, incident review, and any remedy plan.
What Audits Missed
Research notes indicate that internal and third-party audits did not catch the deposit-detection flaw before the loss. That does not prove the audits were careless; it shows the limit of audit scope if reviewers focus on contract code while under-testing bridge-specific business logic. Bridge correctness depends on parsers, indexers, relayers, chain-specific transaction semantics, reserve accounting, and operational controls. A useful audit plan needs adversarial test cases for wrong destinations, duplicate events, malformed metadata, unexpected trust-line behavior, and balance mismatches.
This pattern fits a broader concern in bridge security: public audit reports can miss exploit paths that form between systems rather than inside one contract. A related discussion of blockchain audit gaps is relevant because the defect here was a cross-system validation failure, not a simple private-key theft. Teams should treat audit completion as one evidence point, not as proof that bridge accounting is safe under hostile inputs.
Prevention Measures For The XRP Ledger bridge exploit

Controls That Should Be Mandatory
For the XRP Ledger bridge exploit, the most direct prevention control was destination address validation. A bridge deposit verifier should confirm that the destination account is the bridge’s reserve account, the delivered amount matches the expected asset, the transaction status is final under the source chain’s rules, and the event has not already been processed. Memo or tag fields may help route deposits internally, but they should not be treated as proof that funds arrived.
Reserve reconciliation should run continuously, not only after incident reports. The bridge should compare wrapped supply, pending withdrawals, reserve balance, and observed source-chain deposits. If the reserve falls outside expected tolerance, the system should pause payouts automatically or require manual review under an emergency process. Monitoring also needs to detect velocity anomalies. Ninety-four payouts in 97 minutes from a small reserve should have triggered a control that asked whether accounting state matched real assets.
- Validate destination and delivered amount: Treat metadata as routing information, not settlement evidence.
- Model chain-specific behavior: Test DefaultRipple and trust-line interactions under conditions that are valid on the source chain but invalid as bridge deposits.
- Diversify relayer checks: Relayers should not all rely on one identical unsafe interpretation path.
- Reconcile backing continuously: Compare reserve assets with issued wrapped assets and pause on material mismatch.
- Test negative cases: Include wrong destination, self-transfer, replay, malformed memo, and unexpected account-history cases in audits.
Operational Maintenance After A Patch
A patch that adds destination validation is necessary but not sufficient. Bridge operators should publish a clear incident timeline, describe the verification rule that failed at a high level, and state how reserve accounting will be measured after restart. They should avoid publishing exploit-ready details, but users need enough information to understand whether the patched system now checks delivered assets, reserve balances, and relayer agreement independently.
Operational maintenance also includes drills. A bridge team should rehearse halt authority, user communication, forensic evidence preservation, and regulatory complaint workflows before a live incident. For internal training decks or tabletop exercises, teams that need presentation assets can explore using Free Slideshows for creating related materials. The security point is practical: incident materials should help engineers, support staff, and executives respond from the same verified facts.
XRP Ledger bridge exploit Response Priorities
What Users And Operators Can Verify
The safest response to the XRP Ledger bridge exploit is evidence-based patience. Users affected by bridged XRP should look for signed operator updates, reserve-status disclosures, and precise restart conditions rather than informal claims. This is not financial advice; it is a security practice. Affected users need to know whether backing has been restored, whether withdrawals remain paused, and whether any compensation or remediation process has been formally announced.
Operators of other bridges should treat this case as a test plan. The central question is not whether their relayers can sign with a threshold. The question is whether every relayer is verifying the right facts before it signs. If a bridge cannot prove destination, delivered amount, finality, uniqueness, and reserve consistency, then its signing threshold may only automate a faulty assumption. The incident did not show that bridging is impossible, but it did show that bridge security depends on correct interpretation of source-chain behavior and fast detection of accounting drift.