On October 5, 2026, the FinCEN Crypto Withdrawal changed the policy picture for two digital-asset reporting proposals that had never become final rules. FinCEN withdrew a 2020 proposal covering certain transactions involving convertible virtual currency and unhosted wallets, and it also withdrew a 2023 proposal focused on crypto mixing activity under Section 311 of the USA PATRIOT Act, according to the agency’s withdrawal announcement. For security teams, the key issue is not whether the proposals were popular. The practical question is what monitoring, evidence collection, and customer-risk controls remain when two proposed reporting paths are removed.
This is a security and compliance analysis, not financial advice. The evidence supports a cautious reading: the withdrawal reduces the chance of new explicit reporting duties in these two areas for now, but it does not remove existing Bank Secrecy Act, Suspicious Activity Report, recordkeeping, or risk-based compliance duties for covered institutions. It also does not remove the technical risks linked to self-custody, transaction layering, wallet hopping, cross-chain movement, or services designed to obscure fund flows.
FinCEN Crypto Withdrawal Security Effects
What The FinCEN Crypto Withdrawal Removed
The 2020 unhosted-wallet proposal would have applied to banks and money services businesses handling certain convertible virtual currency or digital-asset transactions involving wallets not held at regulated intermediaries. The withdrawn text would have required identity verification for transactions above US $3,000 involving unhosted wallets, with reporting or recordkeeping duties above US $10,000 over a 24-hour period, as described in the Federal Register notice.
The 2023 mixing proposal targeted a different control point. It would have treated certain crypto mixing activity with a foreign nexus as a primary money laundering concern and required covered financial institutions to report data such as wallet addresses, transaction hashes, and IP addresses. Research notes state that FinCEN viewed the proposal’s definition as expansive and capable of chilling legitimate activity. That concern matters because privacy tools are not all used for crime, yet the same privacy properties can make investigations slower and less certain.
Thresholds That No Longer Became Duties
The FinCEN Crypto Withdrawal means the proposed thresholds did not become new binding duties through those rules. That matters for operational design. A regulated exchange or payment business may still apply wallet-screening controls, collect customer information, and file SARs when facts support suspicion, but the withdrawn rule no longer supplies the specific unhosted-wallet trigger structure that compliance systems might have been built around.
For security teams, thresholds are not just legal numbers. They shape alert logic, escalation queues, analyst staffing, evidence retention, and customer-service scripts. Removing a proposed threshold can reduce false positives in some workflows, but it can also make monitoring less uniform across firms. One business may continue strict controls for unhosted-wallet exposure; another may take a lighter risk-based approach. That unevenness creates practical friction for law enforcement and counterparties seeking consistent records across multiple platforms.
What Remains Under Existing AML Controls
Risk-Based Monitoring Did Not Disappear
The withdrawal did not repeal the broader AML/CFT framework that already applies to covered financial institutions and virtual asset service providers. Existing obligations under the Bank Secrecy Act, SAR requirements, and recordkeeping rules still matter. In practice, this means firms still need defensible policies for customer due diligence, transaction monitoring, sanctions screening, escalation, and incident documentation.
The security challenge is that risk-based monitoring depends heavily on data quality and analyst judgment. A transaction hash may show movement between addresses, but it does not prove control of a wallet by itself. A blockchain analytics label may help triage risk, but labels can be incomplete, delayed, or disputed. A customer explanation may be truthful, incomplete, or false. Good controls treat these inputs as evidence, not certainty.
Teams reviewing their controls after the FinCEN Crypto Withdrawal should focus on defensible process rather than symbolic checks. A useful program documents why a wallet cluster was considered high risk, what data supported the decision, whether the customer was asked for context, and how the case was resolved. For a related discussion of compliance risk around digital assets, see this analysis of self-hosted wallet rule withdrawal.
Operational Limits After The FinCEN Crypto Withdrawal
The FinCEN Crypto Withdrawal therefore shifts more weight to internal control design. That is not necessarily a failure, but it leaves several limits visible. First, unhosted wallets have no regulated operator that can always supply account-owner records. Second, mixing services can break simple transaction-path assumptions by combining, splitting, or delaying flows. Third, cross-platform movement can create gaps when one entity has strong records and another has weaker records or sits outside U.S. supervision.
Research notes also point to stablecoins as a significant risk area. They report that stablecoins accounted for most illicit virtual-asset transaction volume in 2025, and that hundreds of stablecoins were in circulation by mid-2025 with market capitalization above USD $300 billion. Those figures do not mean stablecoins are inherently illicit. They do show why stablecoin monitoring, issuer controls, exchange controls, and wallet-risk review are now central to crypto-security work.
Security Gaps For Wallets And Mixers
Where Investigations Can Slow Down
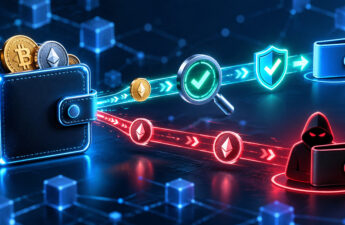
Unhosted wallets and mixers affect investigations in different ways. An unhosted wallet can be controlled by an individual, a business, a service, or a bad actor, but there may be no intermediary with customer records. A mixer may introduce many possible transaction paths, making it harder to link source and destination with confidence. In both cases, investigators may still use blockchain data, subpoenas to regulated platforms, open-source context, victim reports, and public-private cooperation, but the path can take longer.
Research notes say critics warned that the withdrawn rules leave gaps: the unhosted-wallet rule would have addressed transactions involving wallets outside regulated control, while the mixing rule targeted services that obscure transaction paths. That warning is credible from a defensive standpoint, although the policy tradeoff is real. Overbroad reporting can collect data on lawful users, raise privacy concerns, and burden firms with low-value alerts. Underbroad reporting can leave investigators without timely data in ransomware, fraud, sanctions-evasion, or terrorism-financing cases.
Who Carries More Monitoring Burden
The main burden now sits with exchanges, custodians, banks, payment firms, blockchain analytics providers, and compliance teams that must make risk judgments without the withdrawn rule structure. Users are also affected because firms may apply different policies to deposits from self-custody, withdrawals to new addresses, exposure to mixer-linked funds, or stablecoin transfers. A transaction that clears at one platform may be delayed or rejected at another.
- Exchanges and custodians: need consistent wallet-risk policies, escalation records, and clear customer communication.
- Banks and MSBs: need to map crypto-related exposure into existing AML systems without assuming all self-custody is suspicious.
- Investigators: may need more multi-party evidence collection when funds pass through unhosted wallets or obfuscation services.
- Users: should expect more variation in platform checks, especially after large transfers or transactions with unclear provenance.
Security training should reflect that variation. Staff should know how to preserve transaction hashes, timestamps, wallet addresses, customer statements, and case notes without overclaiming what the evidence proves. Teams that brief employees or clients with slide-based material can use the educational resources available at FreeSlideshows to effectively prepare internal presentations on policy changes.
FinCEN Crypto Withdrawal Security Reading
The FinCEN Crypto Withdrawal should be read as a regulatory reset, not as proof that wallet and mixer risks have faded. The October 5, 2026 withdrawal removed two proposed rule paths before finalization, but it left covered firms with the same core task: detect suspicious activity, preserve useful records, and apply controls that can be explained to examiners, partners, and investigators.
A cautious security program should avoid two mistakes. One mistake is treating every unhosted wallet or privacy-preserving transaction as illicit. The other is treating the absence of a new rule as permission to ignore high-risk patterns. Better practice sits between those extremes: document evidence, apply proportional controls, review analytics limits, train staff on uncertainty, and update procedures when official guidance changes.
- Review wallet-risk rules for deposits and withdrawals involving self-custody.
- Define when mixer exposure requires escalation, customer contact, or SAR review.
- Keep records that distinguish blockchain facts from assumptions about wallet control.
- Test monitoring logic against stablecoin, cross-chain, and high-value transfer scenarios.
- Reassess policies after new FinCEN, Federal Register, or supervisory statements.
As of October 20, 2026, the strongest evidence supports a measured position: the withdrawn proposals reduced near-term reporting expansion, but they did not close the security questions around unhosted wallets, crypto mixing, and stablecoin movement. Those questions remain technical, operational, and policy-driven, and they require careful controls rather than slogans.